An untrusted port is a switch port whose received ARP messages are inspected by Dynamic ARP Inspection (DAI) before forwarding or discard. DAI leaves all ports untrusted by default, so ARP arriving from end hosts is checked while non-ARP traffic remains unaffected. section 14.2.1
Use the untrusted state for ports connected to end hosts:
- Inspect ARP messages and discard invalid messages, such as a spoofed ARP reply that does not match the DHCP Snooping binding table. section 14.2.1
- Keep ports connected to PCs untrusted; trust ports connected to network infrastructure such as routers and switches. section 14.2.1
- Avoid confusing DAI and DHCP Snooping: DHCP Snooping trusts ports toward the DHCP server, whereas DAI generally trusts infrastructure-facing ports. section 13.2.1 section 14.2.1
Trusting an infrastructure-facing interface
Configure and verify the port with: interface g0/1; ip arp inspection trust; do show ip arp inspection interfaces. The output should show Gi0/1 as Trusted, while end-host interfaces such as Gi0/2 and Gi0/3 remain Untrusted. section 14.2.1
Figure 14.4 Configuring DAI trusted ports. Ports connected to network infrastructure devices (switches, routers) should be trusted, and ports connected to end-user devices like PCs should remain untrusted.
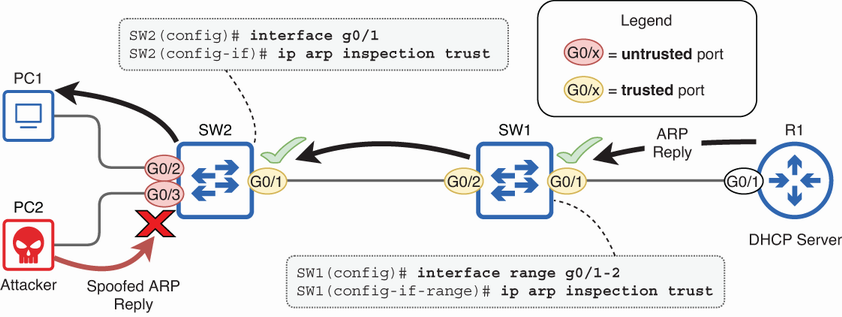
Shows the recommended placement of trusted DAI ports on infrastructure links and untrusted ports on end-user links. section 14.2.1
