An X.509 certificate authenticates a Kubernetes user to the API server. kubectl presents a signed client certificate stored in kubeconfig; the server verifies it against Kubernetes’ built-in certificate authority and maps the request to a username. section 3.1
For Kubernetes administration and CKA preparation, distinguish these operational points:
- Use client certificates for typical human requests made with kubectl. section 3.1
- Treat authentication and authorization separately: the certificate proves identity, while RBAC determines permitted actions such as listing pods. section 3.1
- Contrast user certificates with Service Account tokens, which authenticate pod-to-API-server requests. section 3.1
Figure 3.1 Using a certificate and token to access the Kubernetes API
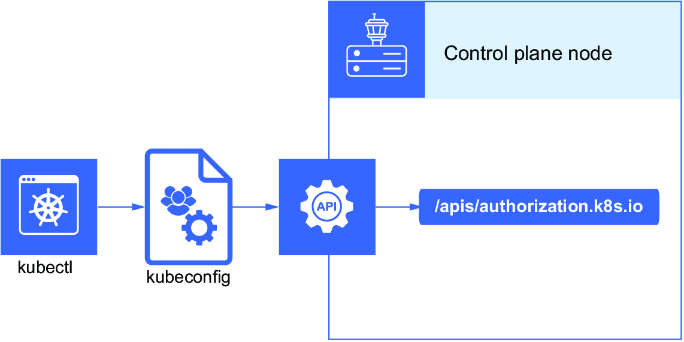
Trace how a certificate and token provide access to the Kubernetes API. section 3.1


