A CI/CD server runs configurable workflows that turn repository changes into repeatable delivery steps. With infrastructure as code (IaC) and version control, it can build and test pull requests before merged changes are deployed to production. This shortens the path from a vulnerability fix to a programmatic Azure deployment while preserving a tracked change history. section 11.3
For security operations, the server is part of a layered delivery process rather than a complete control by itself. A workflow can apply consistent security configuration across Azure resources, such as enabling Microsoft Defender for Cloud plans on subscriptions that host an application. section 11.3.1
Configure an Azure-targeting CI/CD workflow in a deliberate order:
- Create a Microsoft Entra ID service principal with a role and scope that provide the required permissions. section 11.3.1
- Configure the CI/CD platform to use the service principal credentials, storing the generated authentication details as a repository secret. section 11.3.1
- Create a workflow that uses Azure CLI to apply the intended configuration across the relevant subscriptions. section 11.3.1
- Run the workflow and inspect its log output to confirm the automated operation completed. section 11.3.1
Enabling Defender plans across subscriptions
A GitHub Actions workflow can programmatically enable Defender CSPM plans for Azure subscriptions containing an application’s resources. The workflow gives security configuration a repeatable deployment path instead of requiring each subscription to be configured manually. section 11.3.1
Figure 11.4 The GitHub Actions workflow can be used to programmatically enable Defender CSPM plan on your Azure subscriptions.
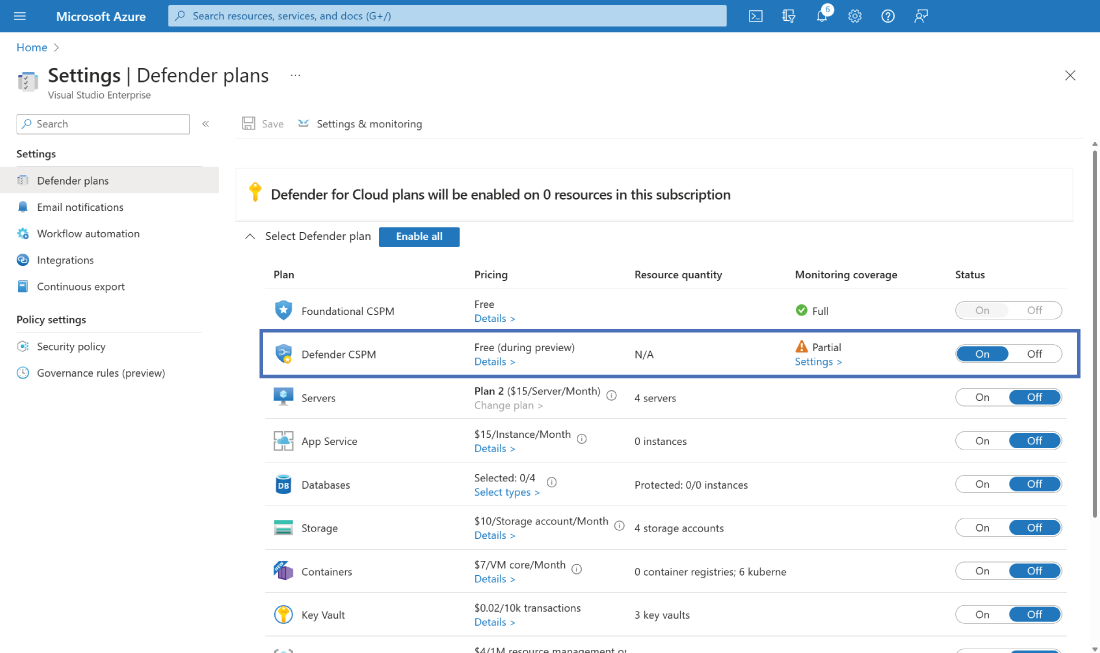
Use the workflow diagram to connect GitHub Actions execution with programmatic Defender CSPM plan enablement on Azure subscriptions. section 11.3.1



