An endpoint is a network-accessible entry point representing an operation or resource in an application. A REST endpoint exposes a route that clients can request, such as GET /hello. section 2.1
Spring Boot can secure an endpoint automatically when the web and security dependencies are present. The default setup applies authentication mechanisms, including HTTP Basic and Form Login, and rejects an unauthenticated request with HTTP 401. section 2.0 section 2.1
Endpoint access can be customized with authorization rules:
- permitAll() allows every request without authentication. section 7.1.1
- hasAuthority() requires one specified authority, while hasAnyAuthority() accepts at least one authority from a list. section 7.1.1
- access() supports custom authorization rules through an AuthorizationManager or an expression such as hasAuthority('WRITE'). section 7.1.1
Protecting /hello
A controller maps GET /hello to a method returning “Hello!”. Without credentials, curl receives 401 Unauthorized. Supplying the generated user and password through HTTP Basic returns “Hello!”. If access requires WRITE, Jane succeeds while John receives 403 Forbidden when only READ is assigned. section 2.1 section 7.1.1
Figure 2.1 Our initial application employs HTTP Basic for user authentication and authorization when accessing an endpoint. It offers a REST endpoint at a specified route (/hello). Upon a successful request, it issues an HTTP 200 status message along with a response body. This instance illustrates the default authentication and authorization mechanisms set up by Spring Security.
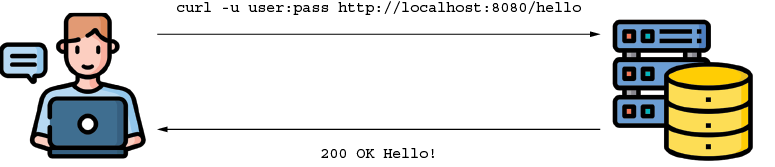
Diagram the route, HTTP Basic credentials, successful HTTP 200 response, and Spring Security’s default authentication and authorization flow. section 2.1

























