liveBook · Manning

Kibana

As explained in Kafka for Architects

Kibana is a visualization and user-interface tool for searching, exploring, and building dashboards over Elasticsearch data.

Kibana is a visual interface for searching, exploring, and building real-time dashboards over log data indexed in Elasticsearch. It provides an SQL-like query interface and a unified view across services. section 5.1.3

Log collection architecture

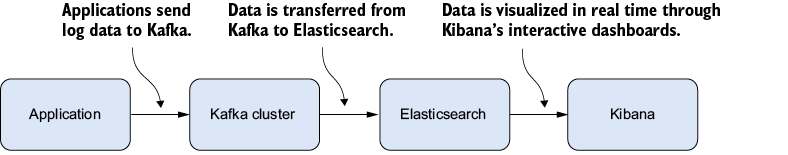
Applications emit standardized log events to Kafka. Kafka forwards them for indexing in Elasticsearch, where Kibana provides interactive search and dashboards. OpenSearch Dashboards can fill the same visualization role with an OpenSearch-based stack. section 5.1.3

Figure 5.6 Conceptual flow for log data collection: log data is sent from the application to Kafka for processing, then indexed in Elasticsearch, and finally visualized in Kibana.
A black and white keyboard with white squares

Description automatically generated

Trace the end-to-end flow from application log events through Kafka and Elasticsearch to Kibana visualization. section 5.1.3


How Kafka for Architects covers it

How deep it goes
Defines Kibana’s interface role and its pipeline position but stops short of implementation details.
Examples
Uses distributed-service logs, SQL-like queries, real-time dashboards, and an application-to-Kafka-to-Elasticsearch flow.
What it assumes
Assumes log events are collected and indexed in Elasticsearch before Kibana interaction begins.
What you can do after
Operate Kibana to query indexed logs and build dashboards that update as log data changes.
How it connects
Connects Kafka, Elasticsearch, log events, dashboards, REST APIs, and OpenSearch Dashboards.

Also explained in

Compare how 3 books explain Kibana →

Related concepts

This explainer was generated by Manning's knowledge graph from the text of Kafka for Architects. The section links point to the parts of the book it draws on.
