Mean time to detect (MTTD) is the average elapsed time from a security incident or breach occurring to its detection. A lower MTTD indicates stronger monitoring and detection capability. It measures the detection stage—not the time needed to respond to or contain an incident. section 6.3.2 section 8.6.1
Use MTTD as an operational-continuity and risk metric: earlier detection gives a team more opportunity to respond before a breach causes further harm. Set a target, compare results over time, and report the gap alongside a proposed action rather than presenting the number alone. section 4.2.2 section 4.2.5
From measurement to decision
A healthcare organization detects breaches within four hours and sets a one-hour target. Its executive report connects that gap to an investment in threat detection. In a separate investment example, AI-based detection reduces MTTD by 40% and is associated with four fewer hours of downtime per incident. These figures make a case for investigation and investment; they do not, by themselves, explain why detection was late. section 4.2.5 section 4.3.2 section 3.6.1
Figure 6.6 On the left, the TechMed risk assessment dashboard before the risk management program is implemented. In this figure, the bottom metrics are displayed as a percentage to indicate the percentage of incidents that were within the predefined target of hours. For example, 40% of the incidents were detected within the 12-hour target detection time. On the right, the risk assessment dashboard after implementing the risk management program.
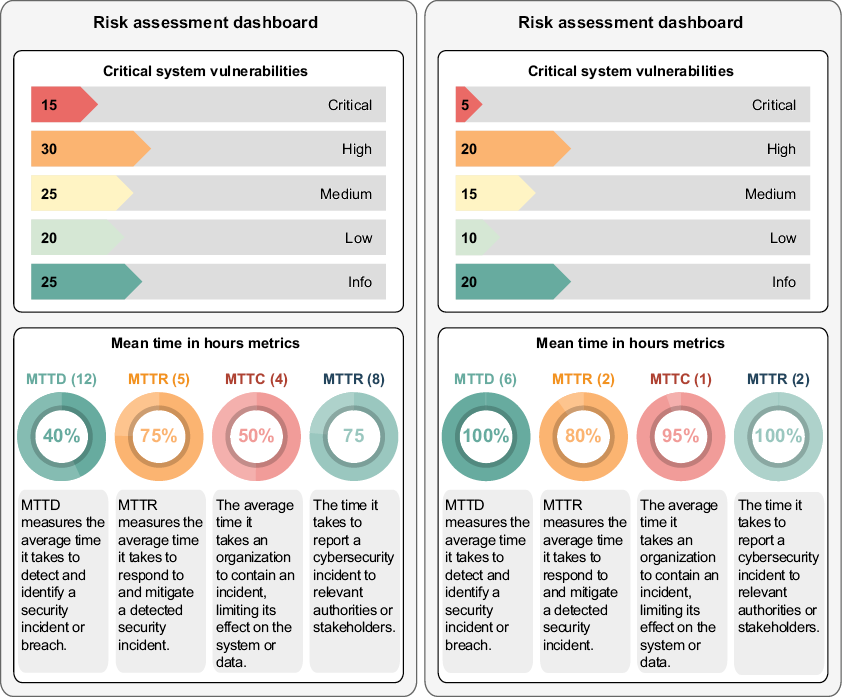
The before-and-after risk dashboard places detection beside response and containment. Read its percentage of incidents meeting a time target separately from the average detection time. section 6.3.3
Investigate outliers with post-incident reviews and team interviews: MTTD alone cannot reveal human, procedural, or decision-making causes of delay. Keep metric boundaries explicit. Time to detect (TTD) can describe one adverse event; incident-identification time measures the later step of confirming a detected event as a legitimate threat. Another incident metric uses “detection time” for the interval from unusual activity to breach confirmation, so check the stated start and end points before comparing reports. section 3.6.1 section 8.6.1 section 9.4.6 section 9.5.2


