A cloud role defines permissions that an authorized identity can assume. In AWS infrastructure pipelines, give each pipeline a role with the permissions needed for its intended changes; give its service account permission to assume that role rather than placing the resource permissions on the account itself. section 6.4.4
Manage pipeline roles through a dedicated first pipeline, and keep them consistent across product accounts. Even if only a few Terraform pipelines configure cloud resources, each needs a dedicated role scoped to the resources it manages. Kubernetes controllers and operators can handle many other platform resources without adding Terraform workflows. section 6.4.4
Figure 6.17 This diagram illustrates how service accounts and permissions are structured across multiple environments—state, sandbox, non-production, and production. Platform engineers interact with these accounts through a centralized SSO integration. Each environment contains a consistent set of roles that pipelines assume to execute changes, ensuring uniformity and security across the platform’s lifecycle.
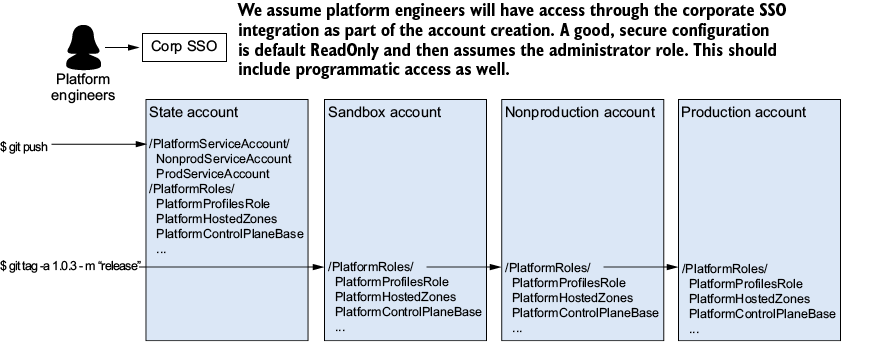
The account diagram shows service accounts assuming a consistent set of pipeline roles across environments. section 6.4.4










