A vulnerability is a weakness in software, configuration, or architecture that an attacker can exploit. In production applications, finding vulnerabilities starts with examining an existing system and its trust boundaries. section 9.1 section 9.2
Common vulnerability areas in a web application include:
- JSON processing weaknesses and outdated dependencies. section 9.2
- Data exposure or tampering across HTTP requests and responses. section 9.2
- SQL injection, weak database access control, and elevation through impersonation. section 9.2
- Weak authentication and web-service access control. section 9.2
Figure 9.1 A threat model for a web application hosted within a company’s network that accesses a database
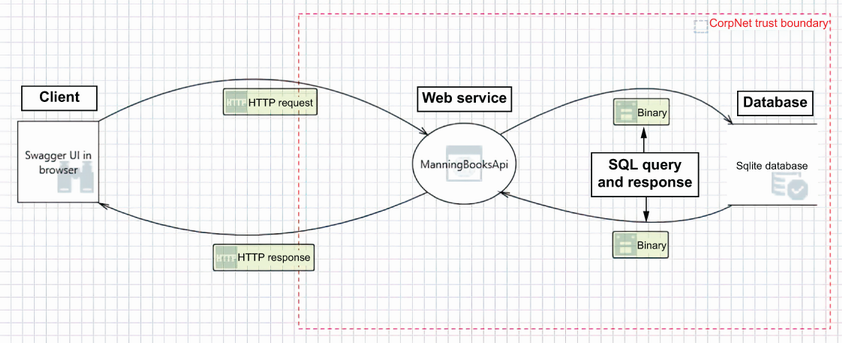
A threat model connects a client, web service, and database, making trust-boundary crossings and their potential vulnerabilities visible. section 9.2















