A vulnerability is a weakness in software that can be exploited to cause unintended or insecure behavior. In practice, vulnerabilities often appear in dependencies, especially old open source libraries whose exploits were discovered after release. section 13.3
Handle vulnerabilities as part of the software delivery workflow:
- Scan container images and their software contents for known vulnerabilities. section 11.5
- Fail the build when security checks find problems, rather than allowing unsafe artifacts to continue toward deployment. section 11.5
- Update vulnerable dependencies and verify that newer versions remain compatible with the application. section 13.3
- Restrict production to digitally signed images that passed the build and security checks. section 11.5
Figure 11.8 A production-grade CI pipeline that adds stages with security gates
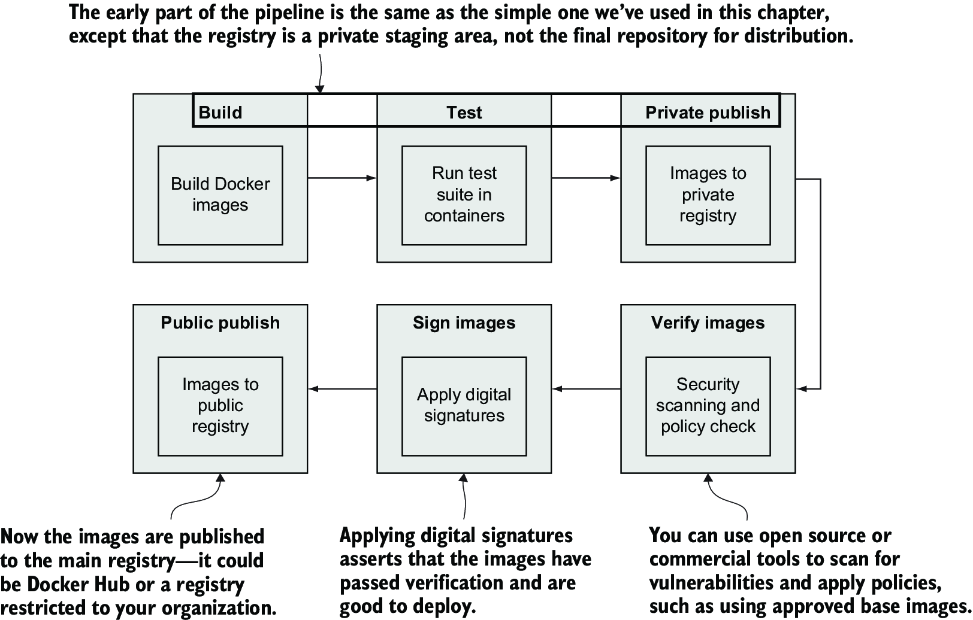
Use the production-grade CI pipeline diagram to trace where vulnerability scans and security gates fit before deployment. section 11.5















