A certificate authority (CA) is a trusted third party in a public key infrastructure (PKI). It verifies identities and digitally signs certificates that link those identities to public keys. section 14.2.6
A certificate works like a digital ID card: its signature helps recipients confirm that a public key belongs to the claimed person, device, or application. This trust helps prevent attackers from substituting their own keys and impersonating trusted parties. section 14.2.6
PKI uses trusted CAs and certificate validation to support trust in digital communications. Protecting key pairs also matters: a compromised key-management entity can expose private keys or enable forged keys and signatures. section 14.2.6 section 14.4
Figure 14.5 Illustration of Alice sending a message to Bob using a Public Key Infrastructure
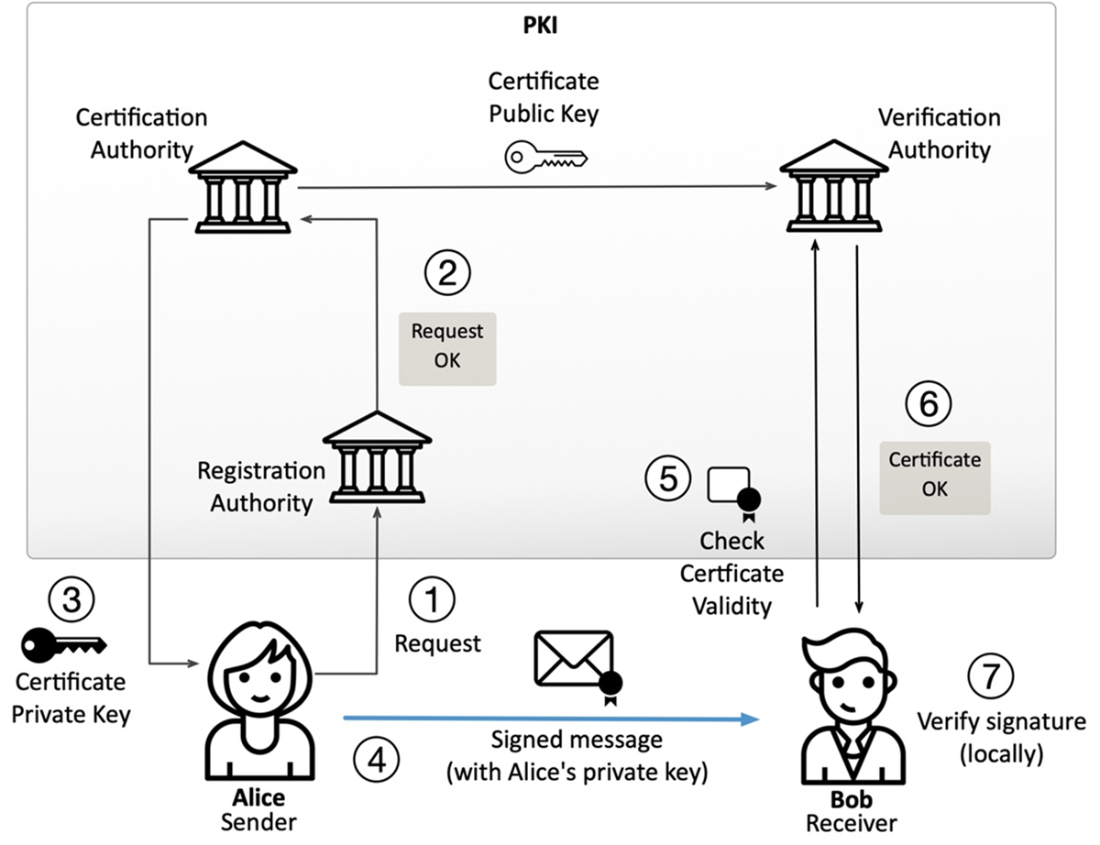
A message-exchange illustration can help trace how PKI supports communication between Alice and Bob. section 14.2.6