Incident response is a documented framework for detecting, containing, investigating, and recovering from incidents. During a ransomware attack, it gives leaders a practical way to establish scope, protect systems, verify backups, and coordinate decisions. section 14.2.1
Use this sequence when an incident is unfolding:
- Confirm that affected systems are isolated so the attack cannot spread. section 14.2.1
- Ask the IT director about affected systems, data, services, ransomware type, backups, and immediate mitigation steps. section 14.2.1
- Brief executives on the incident, operational impact, response actions, legal considerations, communications, and decisions requiring approval. section 14.2.1
- Schedule regular updates so response strategies can change as new information appears. section 14.2.1
Practice with a crisis simulation
Ask an AI assistant: “I’d like you to work with me to do a Disaster Recovery Simulation. How can we get started? I have nothing but a ChatGPT subscription and vague information.” AI can generate ransomware, data-breach, or DDoS scenarios, provide feedback during practice, and identify overlooked response areas. Treat its suggestions as training support, then check them against your actual plans and responsibilities. section 14.2.2
Figure 14.2 A humorous depiction of unpreparedness in crisis
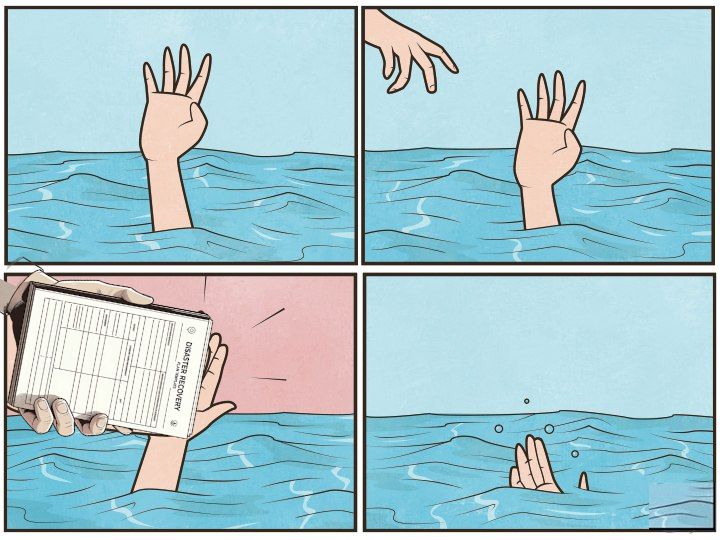
Use the visual reminder of crisis unpreparedness to open a discussion about why documented plans and rehearsals matter. section 14.2.2


