An API key is a credential used to authenticate API requests, typically for nonhuman identities such as applications, services, and devices. Unlike generally short-lived access tokens, API keys may remain valid for weeks or months, so they need expiration and rotation. section 7.1
Treat an API key like a valuable access credential. Hardcoding one into an IoT device can let anyone who obtains the device steal the key and gain unfettered API access. Design for expiration, allow users to rotate keys, and avoid embedding reusable credentials where attackers can extract them. section 1.6 section 7.1
Figure 7.1 During authentication, users exchange their credentials for an access token. During authorization, the API checks whether the access token is valid and the user has access to the requested resources.
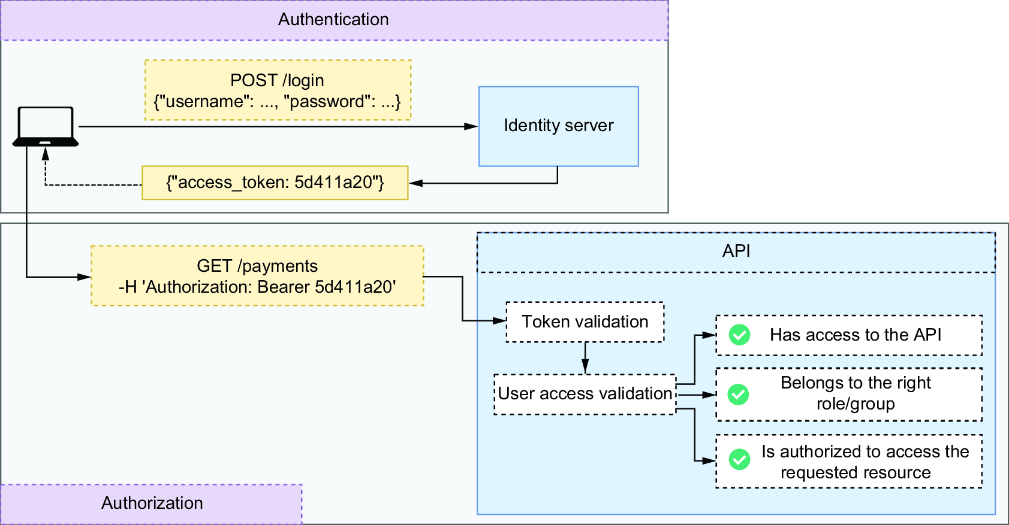
Use the authentication-versus-authorization flow to distinguish proving an identity with a credential from checking access to requested resources. section 7.1












