A recovery point objective (RPO) is the maximum data loss an organization can accept, expressed as the time between a disruption and its latest recoverable copy. RPO turns backup frequency into a business risk decision: a smaller RPO requires more recent recoverable data. section 7.3.4
Use RPO to shape recovery planning:
- Set an acceptable data-loss window for each critical system. section 7.3.4
- Use the target to guide how often backups are made. section 7.3.4
- Track RPO compliance alongside backup success, backup testing, and recovery time objective compliance. section 7.3.5
- Prioritize recovery planning for cyberattacks while recognizing that backups do not by themselves prevent ransomware extortion. section 7.3.4
SecureTech's recovery dashboard
SecureTech Solutions sets targets for regular backups of all critical systems, current RPO compliance, and a four-hour recovery time objective. Its data-security dashboard compares these recovery measures with encryption and backup-protection work, helping leadership identify where recovery readiness still needs attention. section 7.3.6
Figure 7.6 The left side shows the Secure Tech data security dashboard before implementing data protection practices. The right side shows the situation after implementing these practices.
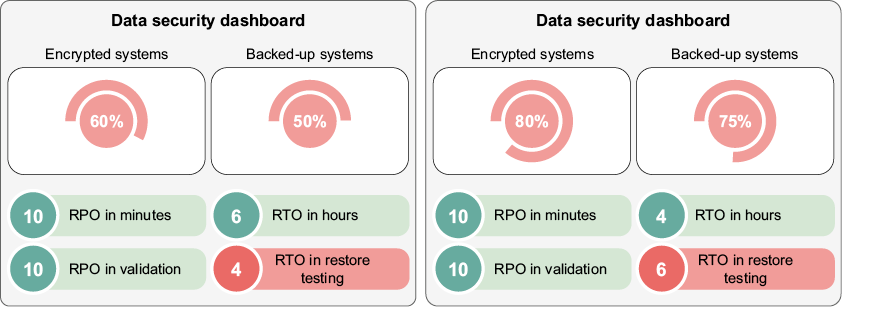
Compare the before-and-after data-security dashboard to connect RPO compliance with broader backup, encryption, and recovery improvements. section 7.3.6




