After a request is authenticated, authorization determines which Kubernetes API actions its user, group, or Service Account may perform. RBAC uses roles and role bindings to control access to resources. section 3.1 section 9.3.2
Choose the permission scope that matches the task:
- Use Roles for permissions within a namespace, and bind them to users, groups, or Service Accounts. section 9.3.2
- Use ClusterRoles for cluster-wide permissions, and bind them to users, groups, or Service Accounts. section 9.3.2
Restricting access to pods
A user can be limited to viewing pods; a role can also allow listing pods in the kube-system namespace. section 3.1 section 9.3.2
Figure 3.3 The RBAC mechanism uses roles and role bindings to prevent unauthorized requests from accessing the Kubernetes API and persisting in etcd.
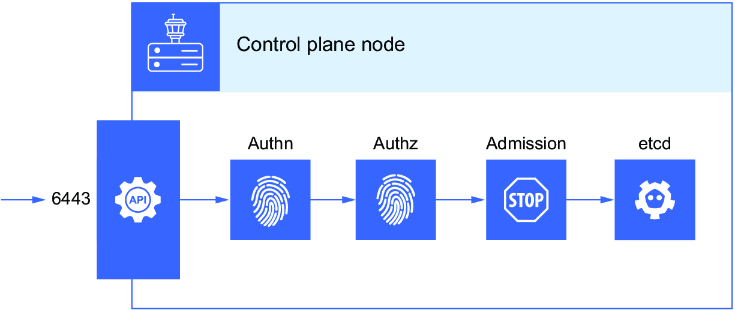
Use the diagram to trace how RBAC roles and bindings restrict requests to the Kubernetes API. section 3.1



























