TLS encrypts HTTPS connections and can verify endpoint identity through certificates. In Kubernetes, an Ingress can terminate TLS at the load balancer, then forward requests to backend Services over HTTP or HTTPS. section 7.2.1
Choose the traffic path according to the security and operational requirement:
- Terminate TLS at the Ingress and use HTTP to the backend over the provider’s secure network; this can reduce application-server overhead. section 7.2.1
- Terminate and re-encrypt at the Ingress when backend connections should also use HTTPS. section 7.2.1
- Use a LoadBalancer Service when encrypted client traffic must pass through unchanged to the backend. section 7.2.1
Configure TLS for an Ingress
Create or obtain a private key and certificate, store them in a Kubernetes Secret, and reference that Secret from the Ingress TLS configuration. A self-signed certificate encrypts traffic but does not verify identity, so browsers warn about it.
Figure 7.5 The Ingress terminates HTTPS (TLS) traffic and can forward it to the serving Pods over plain HTTP or HTTPS connections.
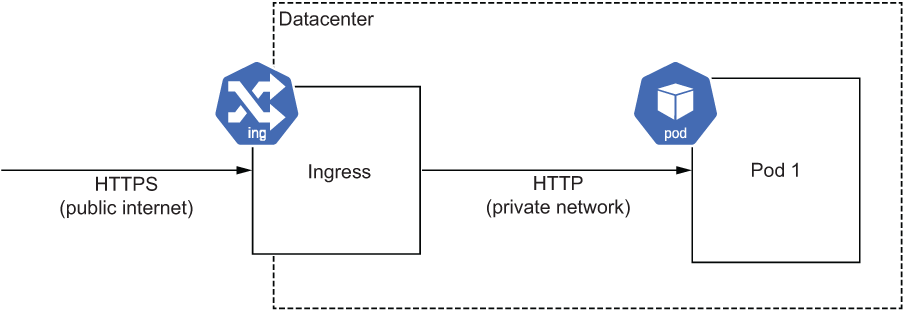
Visualizes TLS termination at the Ingress and forwarding to Pods over HTTP or HTTPS. section 7.2.1














