Security in infrastructure as code means detecting and preventing insecure configurations before deployment, then using configuration to audit access, assess impact, and remediate breaches. This shifts security left: checks catch public access, excessive permissions, exposed secrets, and unsafe network rules during development rather than production. section 1.4.4
Apply security checks to infrastructure and the tools used to manage it:
- Test object-store policies to prevent public read or write access and restrict production access to specific objects. section 1.4.4
- Audit firewall rules so inbound connections come only from known sources. section 1.4.4
- Review external modules for sensitive outputs, third-party data transfers, and compliance-test results before adoption; reassess them after releases. section 13.1 section 13.1.2
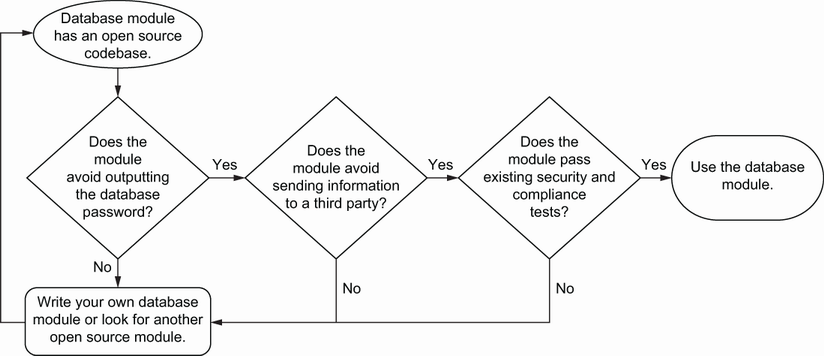
Use the decision flow to evaluate a module or tool’s security before introducing it to an organization. section 13.1.2



























