Authentication verifies an application or user's identity before ScyllaDB grants access. Valid credentials provide a baseline security boundary for database connections and operations. section 9.1.4
ScyllaDB provides three authenticator choices:
- AllowAllAuthenticator accepts every connection and remains the default. section 9.1.4
- PasswordAuthenticator requires every connection to present a valid username and password. section 9.1.4
- TransitionalAuthenticator validates supplied credentials while still permitting anonymous connections, enabling a gradual migration without downtime. section 9.1.4
Enabling password authentication can immediately break applications that lack credentials. Increase the system_auth keyspace replication factor to the cluster's total node count so node unavailability does not prevent login. section 9.1.4
Securing the reviews application
Enable PasswordAuthenticator and CassandraAuthorizer in scylla.yaml, drain and restart the Scylla container, then create a reviews_api role. Configure the Python driver with PlainTextAuthProvider using that role's credentials. The application can connect and query reviews, but cannot drop the reviews keyspace when authorization is configured. section 10.6.1 section 10.6.3
Figure 9.3 In your Scylla cluster are three authenticators: one to allow everything, one that allows only valid users with correct credentials, and one to facilitate transitioning to authentication without downtime.
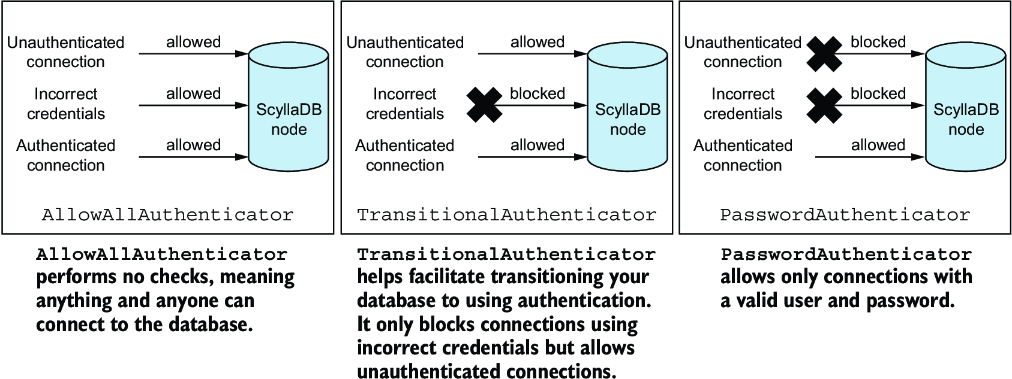
Compare the three connection paths: unrestricted access, credential-enforced access, and transitional access. section 9.1.4

































