A query is a structured request that retrieves or modifies database data. In a Spring Data repository, it can combine a search condition with an authorization condition so the database returns only records the current user may access. section 12.3
Filtering after retrieval with @PostFilter is usually inefficient: findAll() can load every record before application code removes unauthorized rows. Put the ownership condition directly in the query instead. section 12.3
Owner-restricted product query
A repository query can match a requested product name and bind the authenticated username to the owner condition: SELECT p FROM Product p WHERE p.name LIKE %:text% AND p.owner=?#{authentication.name}. A request by nikolai for products containing c returns candy; a request by julien returns chocolate. section 12.3
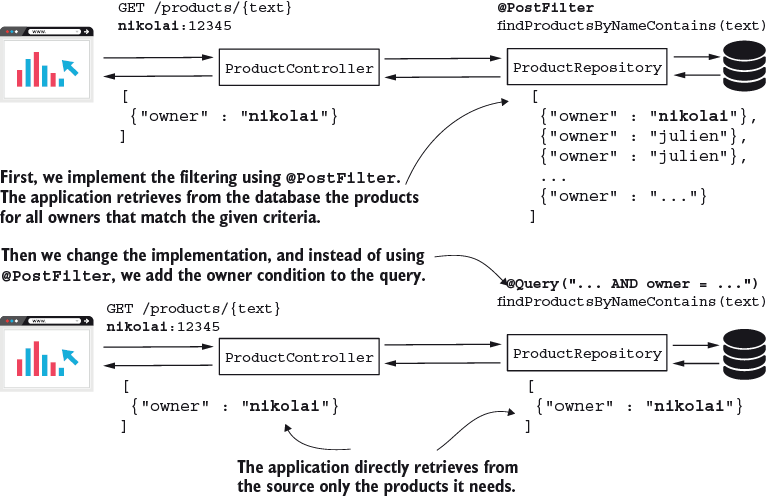
Figure 12.10 In our scenario, we start by implementing the application using @PostFilter to filter products based on their owner. Then we change the implementation to add the condition directly on the query. This way, we make sure the application only gets from the source the needed records.
Compare post-retrieval filtering with a query that restricts records at the data source. section 12.3
























