CI/CD is an automated workflow for validating, reviewing, packaging, and deploying authorization policy changes. A pull request can trigger schema validation, static analysis, and tests before approved policies reach runtime enforcement. section 10.2.4 section 14.2.2
A policy CI/CD workflow typically:
- Checks syntax, schemas, static analysis findings, expected behavior, and test coverage. section 10.2.4 section 14.2.2
- Records review, approval, version history, and the reasoning behind each policy change. section 10.5 section 14.2
- Builds a versioned or signed bundle and publishes it to a policy store or policy administration point for runtime distribution. section 10.2.4 section 14.2.3
A policy change from pull request to runtime
When Bob submits a policy pull request, the pipeline validates action names and schema attributes, runs analysis and tests, and blocks merging on failure. After approval, it creates a signed Cedar bundle, publishes it to the policy store, and enables the authorizer to evaluate requests with the reviewed version. section 10.2.4
Figure 10.6 Continuous integration for policies. Bob’s pull request triggers validation, analysis, and testing. After the checks pass, his changes are merged, bundled into a signed package, and published to a policy store, where the authorizer uses them to evaluate requests at runtime.
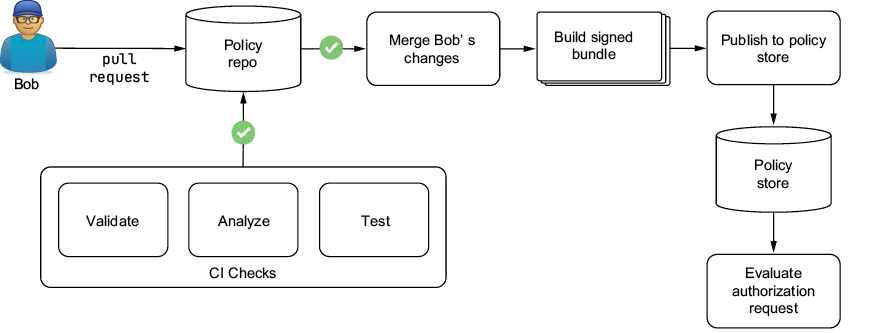
Follow the flow from pull-request checks through merging, signed bundling, policy-store publication, and runtime authorization. section 10.2.4





























