CI/CD is an automated practice for frequently integrating code changes and testing APIs before delivery. Its security role is to prevent insecure APIs from being released. section 1.5
A security-conscious API pipeline should:
- Run fuzz testing against the API specification. section 1.5
- Use API security testing tools to identify insecure behavior. section 1.5
- Execute integration tests that validate expected behavior and simulate user flows. section 1.5
- Support monitoring, observability, alerting, and rapid detection or blocking of malicious behavior after deployment. section 1.5
Figure 1.6 Security by design fits into every step of the API development cycle. It encourages us to approach design, implementation, testing, and operations from a security point of view.
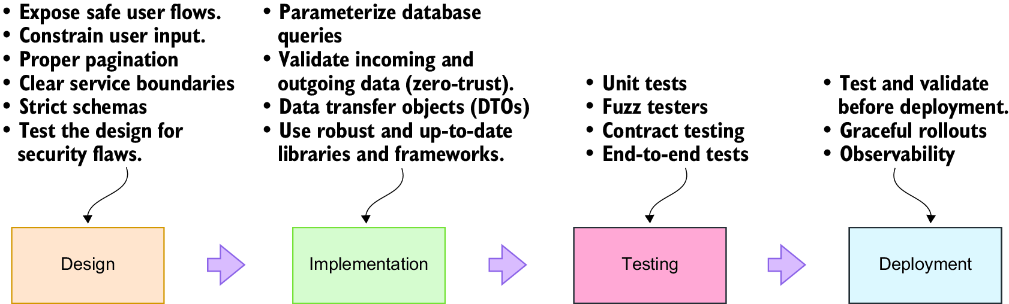
Security by design spans API design, implementation, testing, and operations rather than stopping at deployment. section 1.5





























