Continuous improvement uses feedback and measured results to refine cybersecurity practices. Regular reviews can reveal gaps, recurring problems, or controls that need adjustment as threats and organizational needs change. section 6.4 section 2.5.1
Turn the feedback loop into decisions:
- Set measurable goals tied to business objectives and security risks. section 3.1.1
- Track relevant metrics regularly, looking beyond raw counts to severity, resolution time, and longer-term trends. section 3.1.1 section 11.3
- Review findings, adjust security measures, and monitor whether the changes work. section 11.3
Recurring vulnerabilities
If vulnerabilities keep resurfacing despite mitigation, investigate whether a systemic issue remains. Set a measurable reduction target, review progress, and adjust security measures based on the results. section 3.1.1 section 11.3
Figure 3.1 Security metrics program at a high level, showing key feedback loops
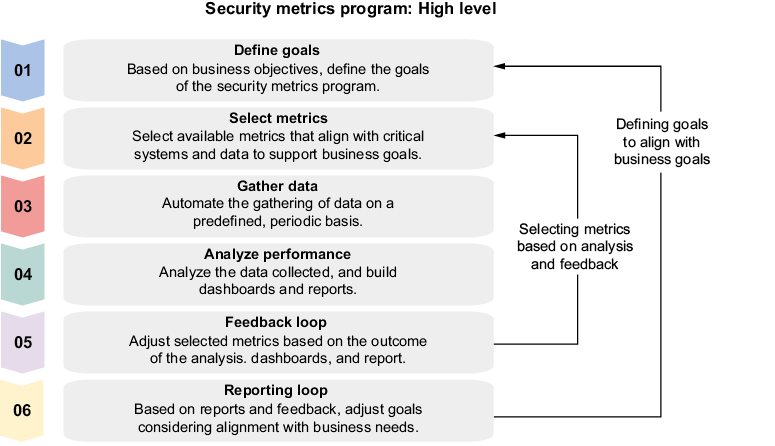
The diagram maps feedback loops into the selection of security metrics and goals. section 3.1.1





























